Review the consent screen
The consent screen will be rendered by Apaleo, as part of the flow described below. Request your API credentials (the ones which work for all hotels) and tell us in the comments:
| API Credentials | What’s this? |
|---|---|
| Client name | Your application’s name, used on the consent screen |
| Scopes or permissions | The access your app needs. For a scope client, these are scopes: they define the type of protected resources a connected app can access, and they are included with the OAuth tokens during the authorization flow. For a fine-grained client, these are permissions, per API: they are shown to the hotel on the consent screen and enforced by the APIs, and they are not part of the scope in the OAuth tokens. Check our Swagger documentation, where each API operation describes which scope or permission is required. |
| Redirect url | It is where users are redirected after successful authorization. It is the connected app’s callback URL. If further setup is required to establish the connection to Apaleo, such as mapping of fields or other configuration, it is a good idea to redirect the user there. Ensure the redirect URL can be called, and is using https. |
We will review the data to ensure that all will work okay and get back to you within a few days.
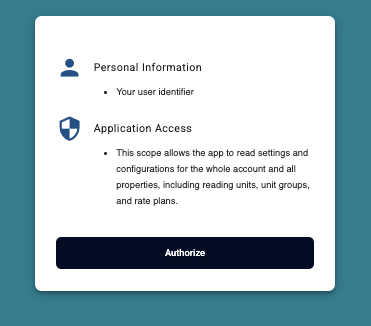
This is how an example consent screen looks like:
What the hotel sees and chooses
What the hotel sees on the consent screen depends on how you registered your app.
- Scope client: the screen lists the scopes your app requests. The hotel approves them for the whole account.
- Fine-grained client: the screen has a Property access step. The hotel chooses All properties (all current and future properties of the account) or Only selected properties (at least one, picked from a searchable list). The screen then lists the permissions your app will have on those properties, with a readable name and the permission key.
Users don’t need to be account admins to connect a fine-grained app. A user can connect it as long as their Apaleo role and property access cover the access your app requests. If they don’t, the connection is blocked at this step.
Hotels can change which properties your app can access later, from Apps > Connected apps in Apaleo. The change applies right away.
For how this fits into the authorization flow, see OAuth 2.0: Authorization code grant flow.