Share a simple client app (developer accounts only)
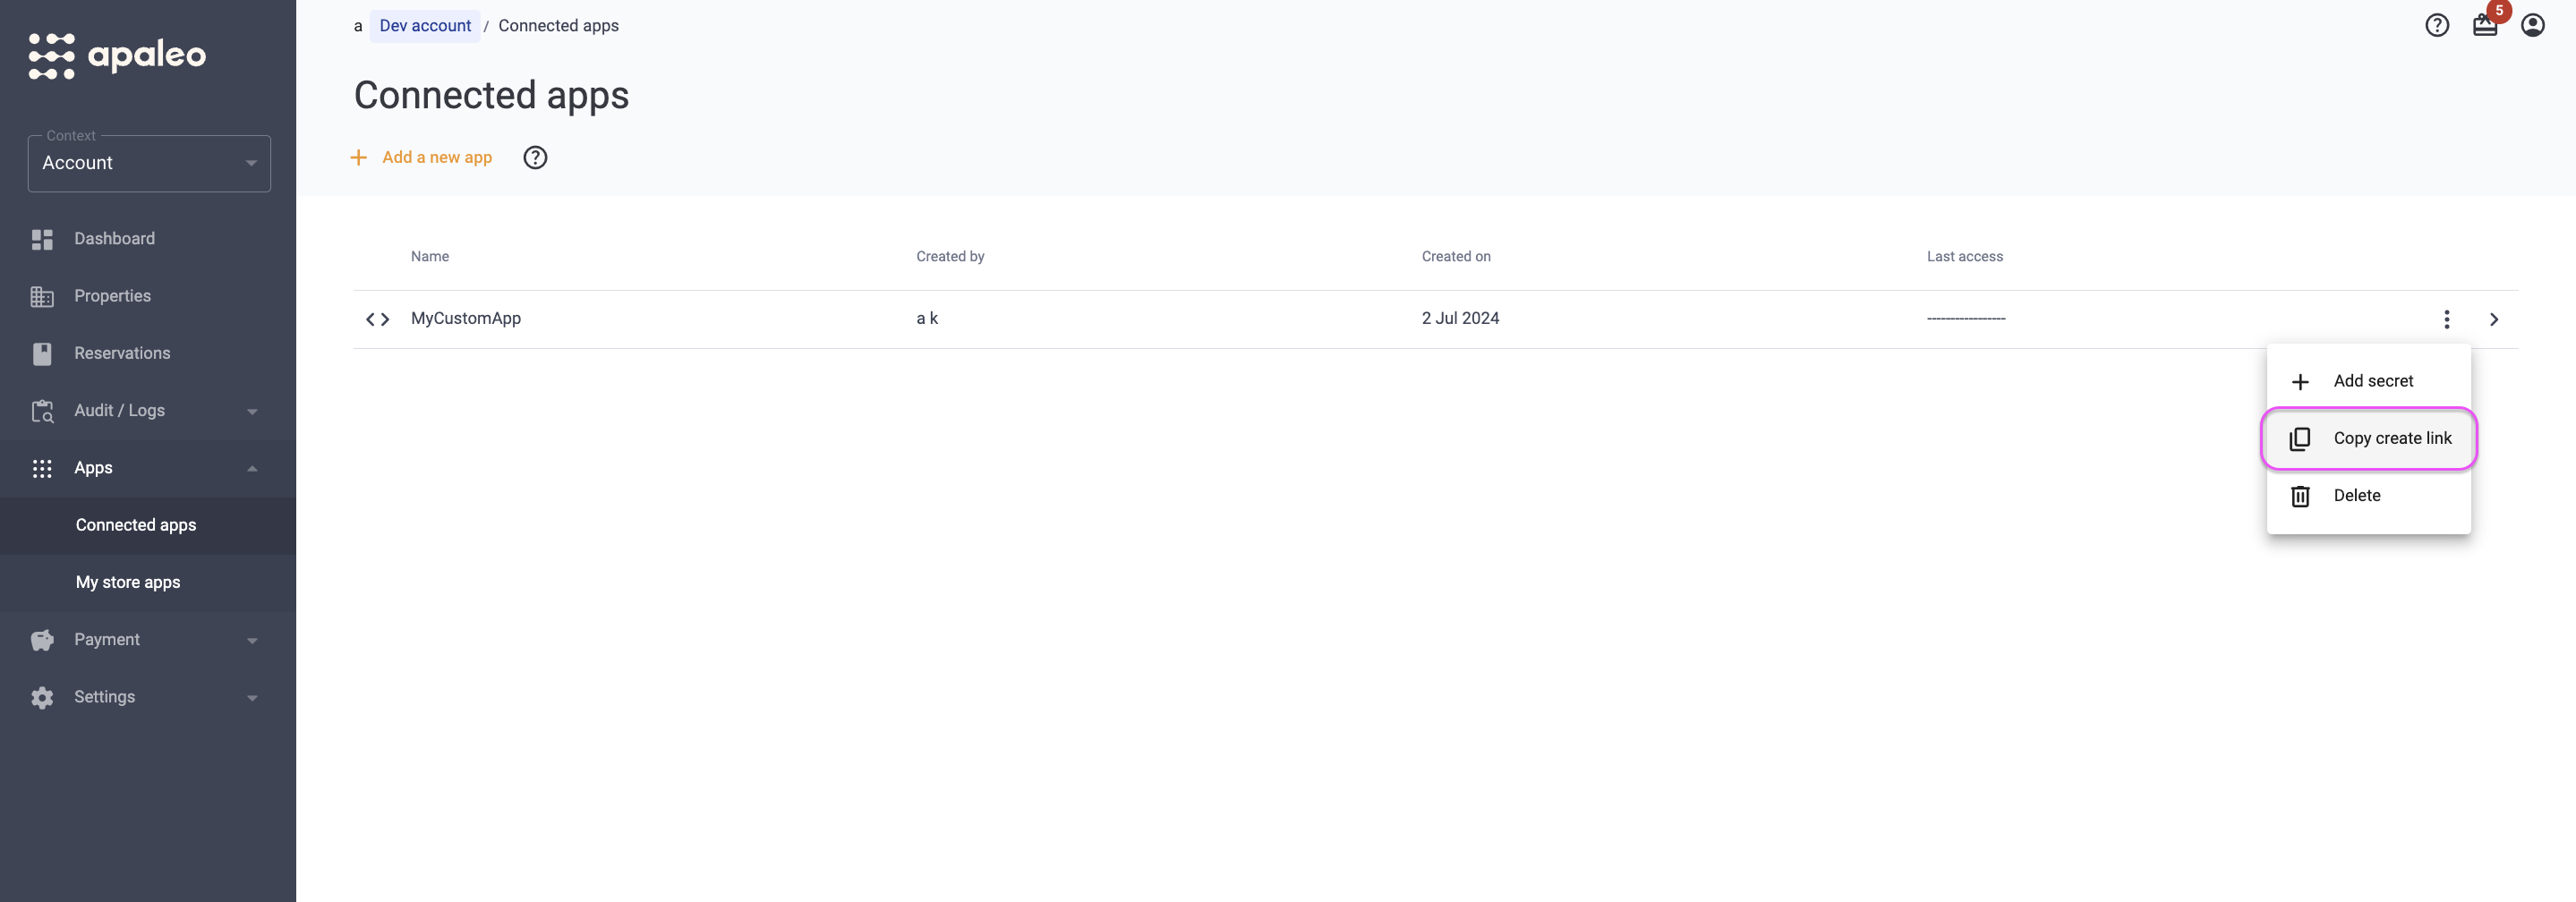
If you have created a simple client and want to share it with a hotel, you can easily do that using the Copy create link feature. It creates a copy of the client in hotel’s account.
To share a simple client:
-
Log into the Apaleo Dashboard with your Apaleo developer credentials.
-
Navigate to the Apps section and click Connected apps.
-
On the connect clients page, select the app to use the Copy create link as follows.
-
Send this link to the hotel.
-
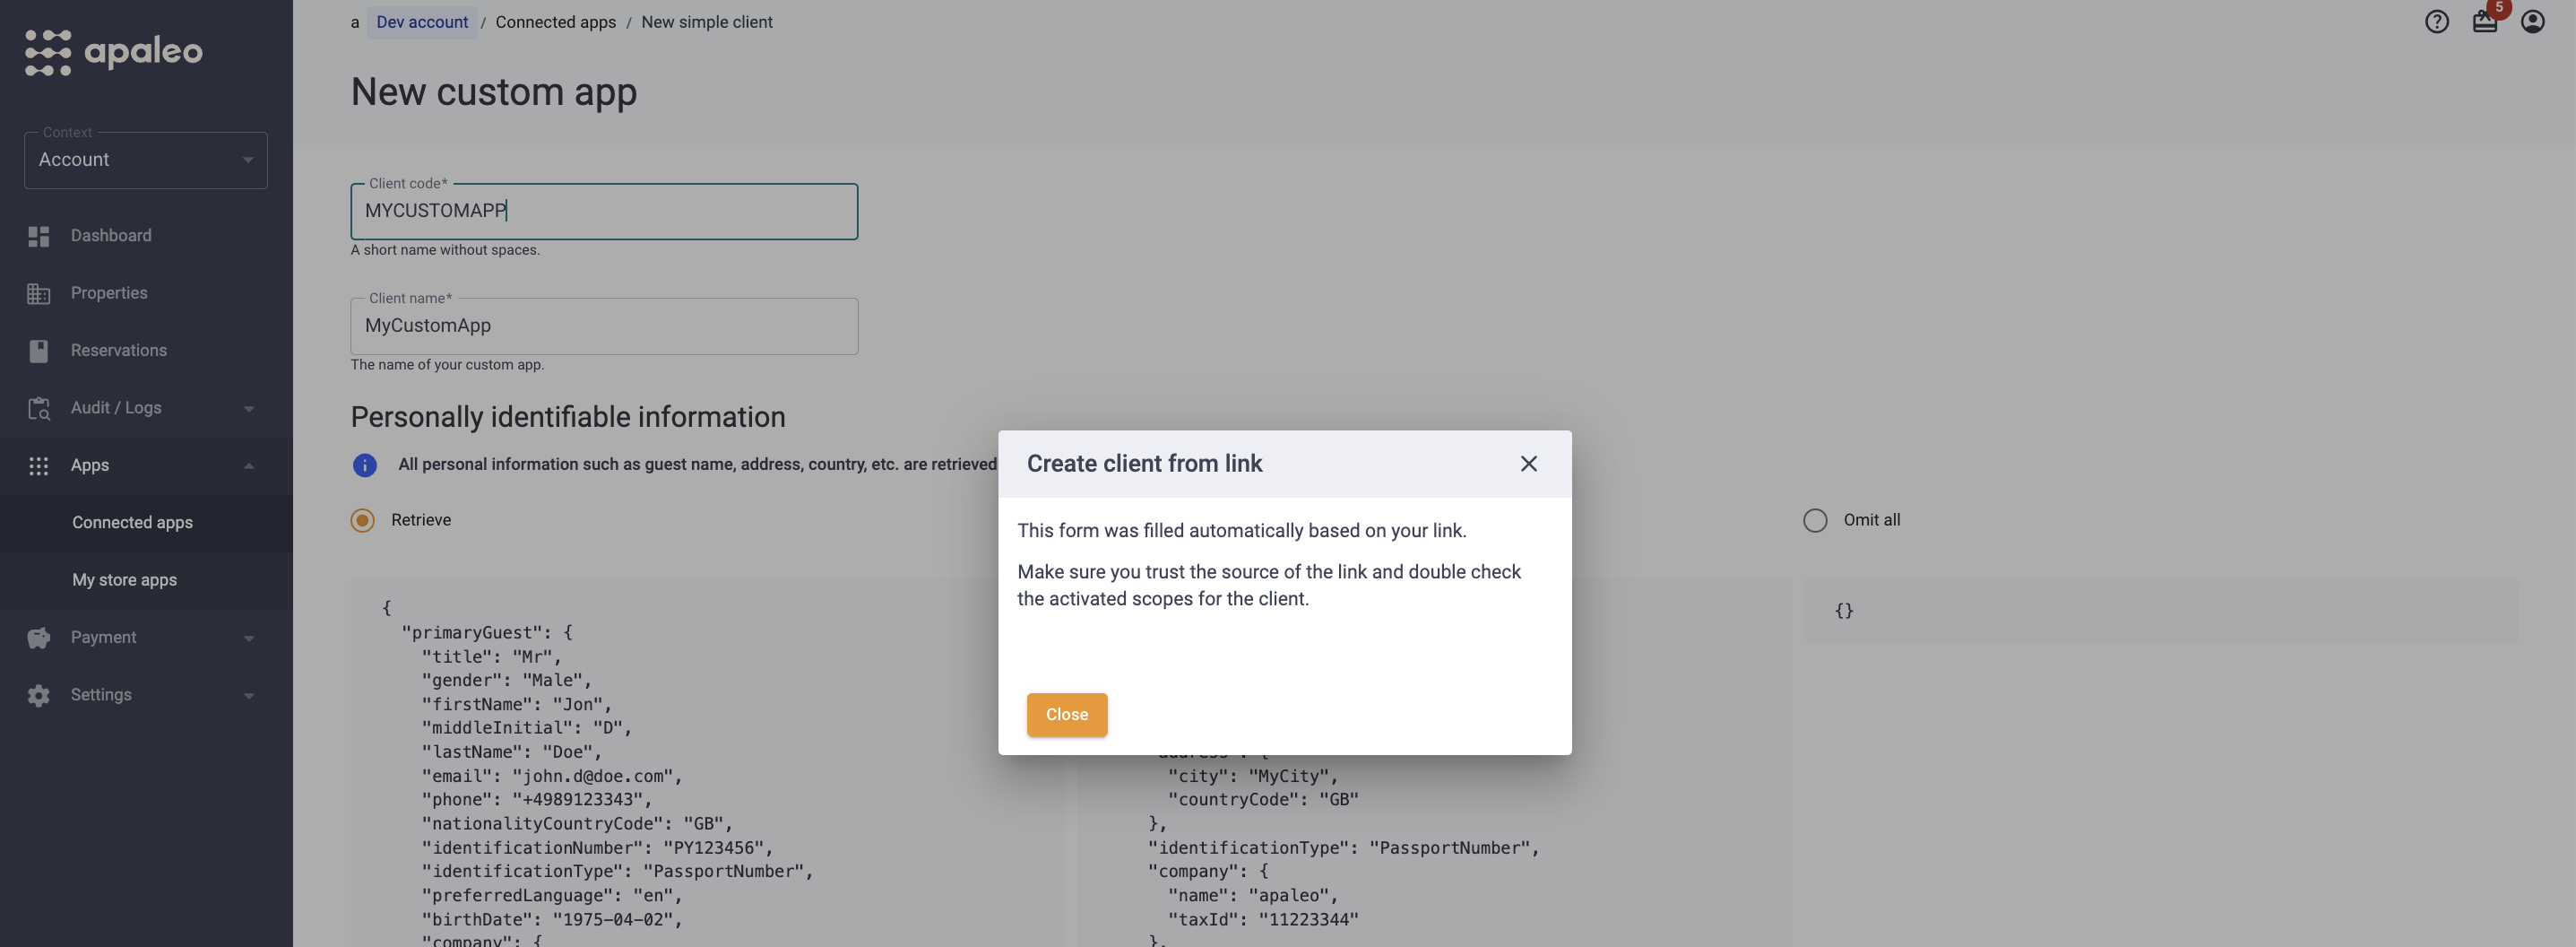
On clicking the link, the hotel will get the following message.
-
On this page, the hotel has to review the following details:
Field Description Client code Unique key for the client application. Client name Human-readable string name of the client application. Personally identifiable information Personal information that is retrieved such as guest name, address, country, etc. Secrets Description of your secret. Client access How the app’s access is granted: a scope client or a fine-grained client. You chose this when you created the app, and it can’t be changed. Scopes or permissions The access the app needs: scopes for a scope client, or permissions per API for a fine-grained client. For a fine-grained client, the permissions you configured are copied to the hotel’s app. Property access Fine-grained clients only. The hotel selects which of its properties the app can access: All properties (all current and future properties of the account) or Only selected properties (at least one). The properties you selected in your developer account don’t carry over. -
Save the app.

-
Keep in mind that the hotel must send you back the
client Idandclient secretafter creating them. Please make sure to transfer those via a secure channel.- Client ID - This identifies the client responsible for the OAuth request. A unique key for the client application.
- Client Secret - A client secret is a secret known only to your application and the authorization server. It protects your resources by only granting tokens to authorized requestors. Always store the client secret key securely; never reveal it publicly! If you suspect that the secret key has been compromised, regenerate it immediately by adding a new secret to the client application.